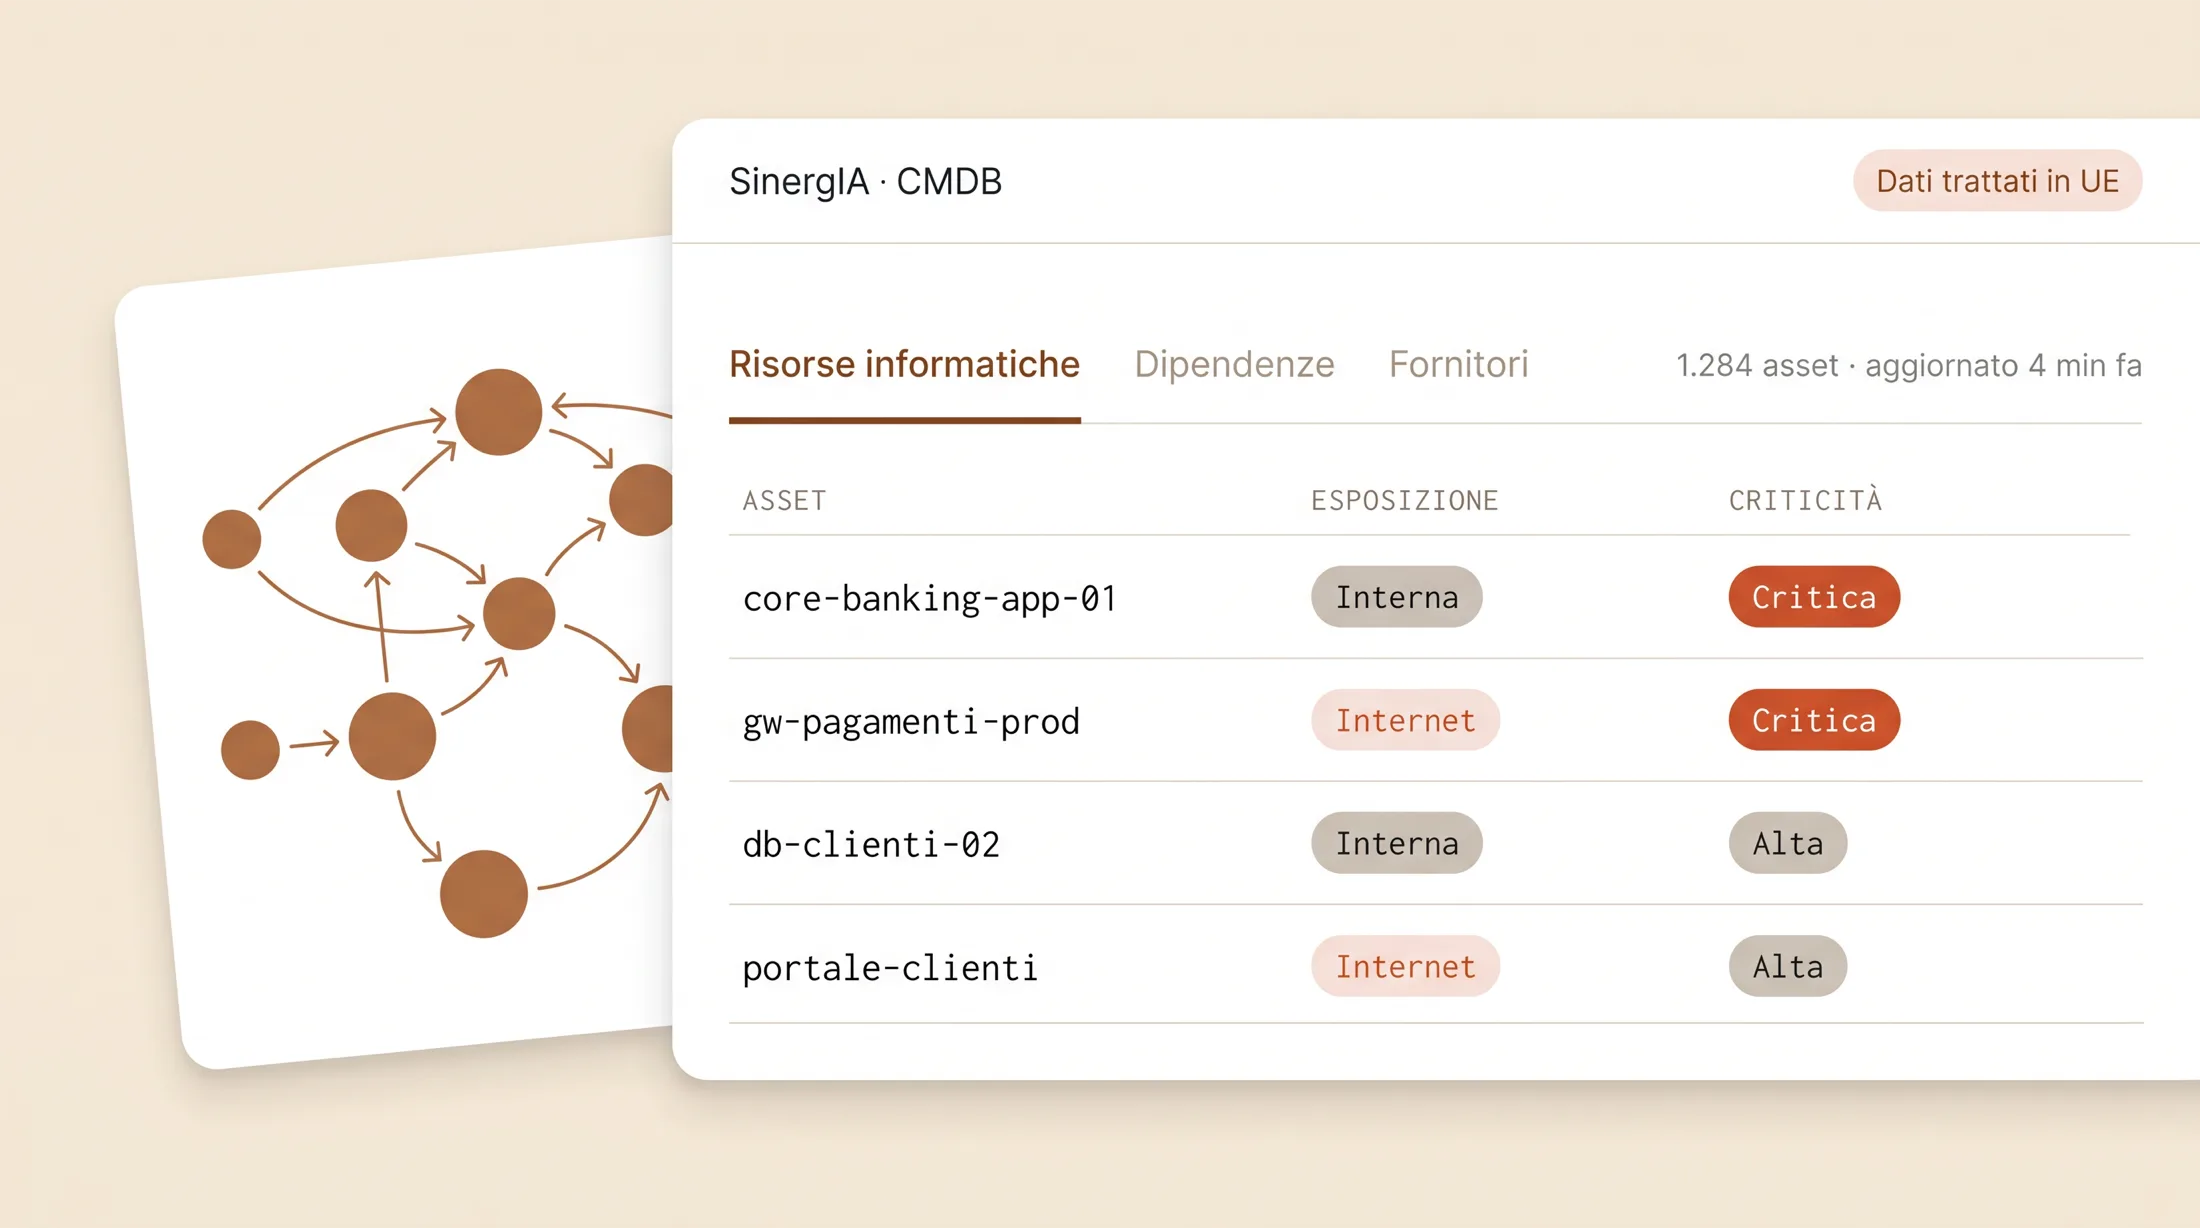

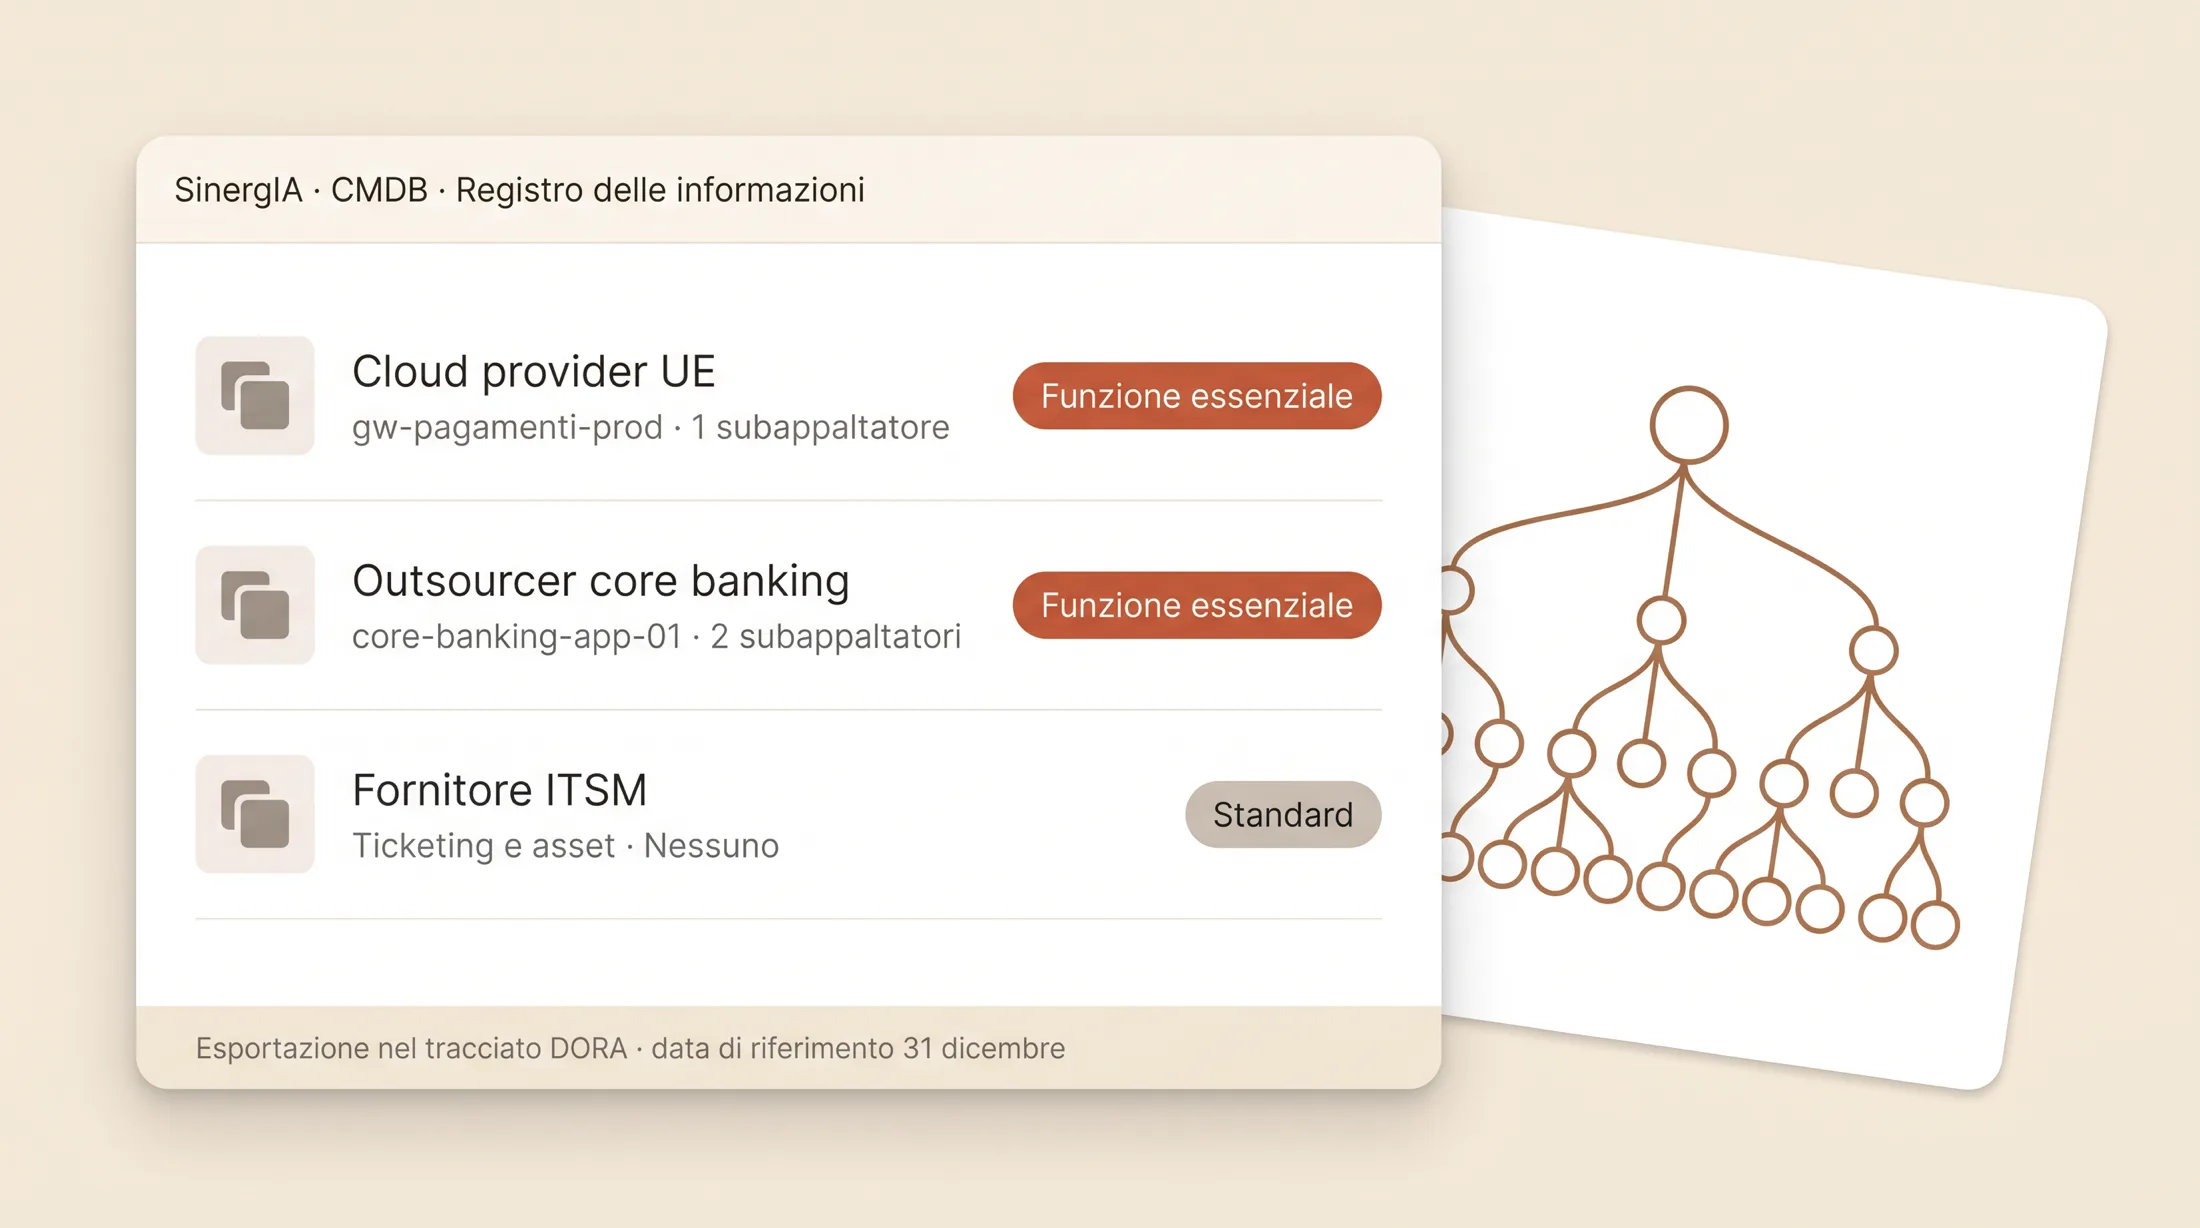
What do I need to know about gw-pagamenti-prod?
gw-pagamenti-prod is internet-facing and classified as critical. What matters right now:
- CVE-2026-3184 open for 6 days — vendor patch already available.
- Last release: 22 August, version 4.2.1.
- Depends on 3 internal services and 1 EU cloud provider.
It's at the top of the remediation queue. Want me to draft the change request?